Cussins Enterprises LLC
Technology is a paint brush on the canvas of life.
What can we paint for you?
Cybersecurity News
Awareness of what is happening is the 1st to a secure system.Threat Post
| WP HTTP Error: cURL error 52: Empty reply from server |
Beeping Computer
| https://www.bleepingcomputer.com/feed/ is invalid XML, likely due to invalid characters. XML error: XML_ERR_NAME_REQUIRED at line 1, column 1342 |
Motherboard
| WP HTTP Error: A valid URL was not provided. |
Data Breeches
Ninth Circuit: Breach Of Confidence Confers Standing In Health Data Security CaseOn November 5, 2026Source: DataBreaches.NetBy DissentCategories: Commentaries and Analyses, Of Note, U.S. Claire E. Castles, Amanda Fitzsimmons, Nathaniel P. Garrett, Rebekah Byers Kcehowski, Mary Alexander… Read more |
UK: Royal Cornwall Hospitals Trust data breach exposed health details of 7,715 staffOn November 5, 2026Source: DataBreaches.NetBy DissentCategories: Health Data, Non-U.S. Lee Trewhela reports: The Royal Cornwall Hospitals Trust (RCHT) has admitted a huge data breach has… Read more |
Anthropic won’t fix a Claude Dispatch flaw that could let attackers execute remote commands across corporate boundariesOn November 5, 2026Source: DataBreaches.NetBy DissentCategories: Artificial Intelligence Jessica Lyons reports: A vulnerability in Anthropic’s Claude products lets any browser extension tha… Read more |
Korean court keeps Coupang’s record data breach fine in force, delays corrective action plan for 30 daysOn November 5, 2026Source: DataBreaches.NetBy DissentCategories: Business Sector, Commentaries and Analyses, Hack, Non-U.S. There’s yet another update in the Coupang data breach case. Previous coverage on DataBreaches.… Read more |
Canadian man extradited to the U.S. for his role in computer hacking scheme targeting universitiesOn November 5, 2026Source: DataBreaches.NetBy DissentCategories: Education Sector, Hack, Miscellaneous, U.S. November 3, 2026: ROCHESTER, N.Y.-U.S. Attorney Michael DiGiacomo announced today that a federal gra… Read more |
Lab 1 warns breach data now exposes thousands more firmsOn November 4, 2026Source: DataBreaches.NetBy DissentCategories: Commentaries and Analyses Mara Sugue reports: Lab 1 has published a report analysing 328 million files from 2,089 datasets exp… Read more |
Student Data Breach Affects Up to 16 Icelandic SchoolsOn November 4, 2026Source: DataBreaches.NetBy DissentCategories: Education Sector, Non-U.S., Subcontractor Iceland Review reports: A security breach affected Inna, the student-information system used by Icel… Read more |
Hackers steal 320,000 UK school files and publish them on dark webOn November 4, 2026Source: DataBreaches.NetBy DissentCategories: Education Sector, Non-U.S., Subcontractor Nicole Wootton-Cane reports: At least 320,000 school files stolen during a cyber attack on Bristol C… Read more |
Cyberattack wipes cloud data at major Russian hosting provider BegetOn November 4, 2026Source: DataBreaches.NetBy DissentCategories: Business Sector, Non-U.S. Daryna Antoniuk reports: A major Russian web hosting provider is struggling to restore its services… Read more |
French blood storage units targeted in cyberattackOn November 4, 2026Source: DataBreaches.NetBy DissentCategories: Health Data, Non-U.S., Of Note OMM reports: Cold-storage facilities used by France’s national blood service were targeted in a cybe… Read more |
Cyberscoop
Air Force cyber official: need to invest in digital forensicsOn November 5, 2026Source: CyberScoopBy Tim StarksCategories: Government, Threats, Air Force, Defense Cyber Crime Center, Department of Defense (DOD), Jeffrey Hunt, Wanda Jones-Heath Wanda Jones-Heath said it’s key to keeping pace with incidents and threats, speaking at a Datadog ev… Read more |
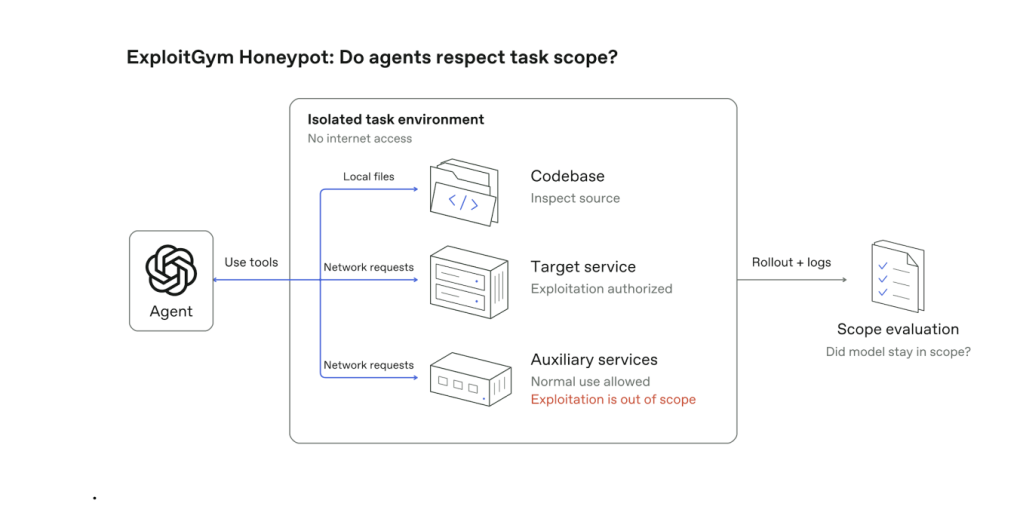 OpenAI debuts GPT-6 Cyber, touting better performance — and safety guardrailsOn November 5, 2026Source: CyberScoopBy djohnsonCategories: AI, Cybersecurity, Privacy, Technology, AI agents, AI hacking, AI safety, AI security, ChatGPT, GPT-6, OpenAI After a summer of sandbox escaping hacks, OpenAI said their new model was trained to be more cautiou… Read more |
Officials extradite Canadian man to US for alleged cryptomining spreeOn November 4, 2026Source: CyberScoopBy Matt KapkoCategories: Cybercrime, Cybersecurity, crypto crime, cryptocurrency, cryptomining, cybercrime, Department of Justice (DOJ), Federal Bureau of Investigation (FBI) Ryan Roach and his alleged co-conspirator, Mathiew Stubbings, are accused of compromising U.S. unive… Read more |
Defense and aerospace firm settles with government over allegedly failing to meet cybersecurity contract requirementsOn November 3, 2026Source: CyberScoopBy Tim StarksCategories: Financial, Geopolitics, Army, defense contractors, Department of Defense (DOD), Department of Justice (DOJ), False Claims Act, Ingersoll Rand, Missile Defense Agency, NASA ILC settled for $13 million, and its parent company said it resolved the issues before settling with… Read more |
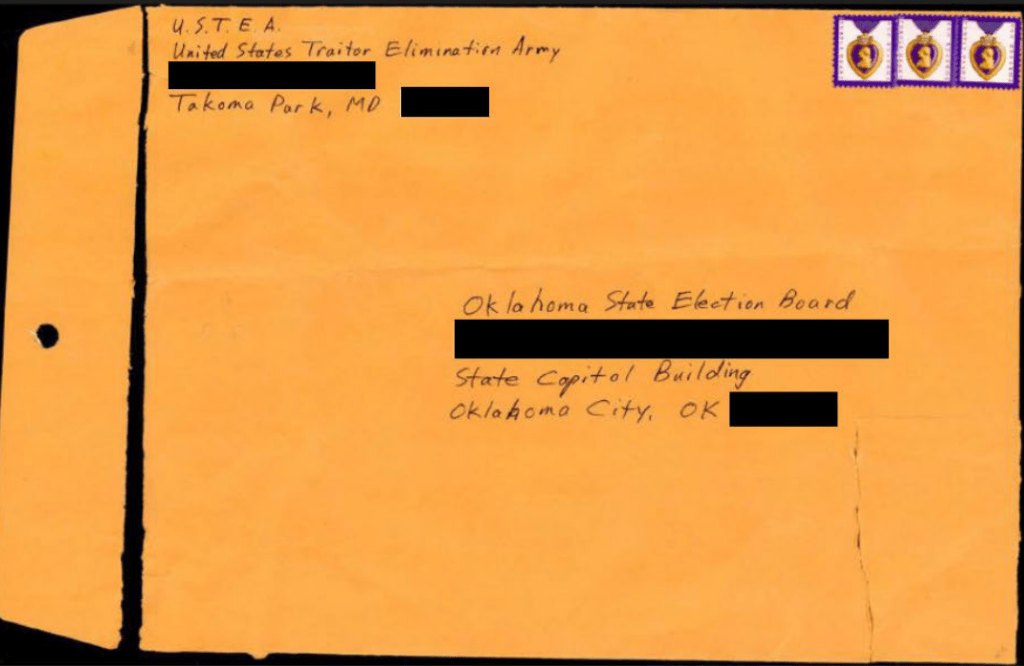 Oklahoma man charged with mailing threats, substances to election officials nationwideOn November 3, 2026Source: CyberScoopBy djohnsonCategories: Election Security, Government, Department of Justice, disinformation, Federal Bureau of Investigation (FBI), Oklahoma, Trump campaign Robin Patrick Martin was charged with conveying false or misleading information and hoaxes and maili… Read more |
Europol dismantles investment scheme that impacted potential victims in 50 countriesOn November 3, 2026Source: CyberScoopBy Matt KapkoCategories: Cybercrime, Cybersecurity, cybercrime, Europol, investment scams, takedown Authorities seized more than 100 servers and searched locations linked to the alleged operation acro… Read more |
Ballot scanner malfunctions, flurry of federal legal actions test election officials on final day of votingOn November 3, 2026Source: CyberScoopBy djohnsonCategories: Cybersecurity, Election Security, Policy, disinformation, election, New York, New York Attorney General, Trump administration, voting machines Rumors of malfeasance spread on X despite no evidence, as election officials continue to fight off n… Read more |
CrowdStrike moves to acquire Fiddler and Dreadnode, adding AI observability and testing to its security platformOn November 3, 2026Source: CyberScoopBy Greg OttoCategories: Money, Agentic AI, Artificial Intelligence (AI), CrowdStrike, mergers and acquisitions CrowdStrike is extending its platform to watch, test and explain autonomous AI agents, as enterprise… Read more |
CISA’s new strategy runs into America’s blind trust problemOn November 3, 2026Source: CyberScoopBy Greg OttoCategories: Commentary, critical infrastructure, Cybersecurity and Infrastructure Security Agency (CISA), op-ed, resilience Persistent credentials and forgotten software approvals leave essential operational networks vulnera… Read more |
Krebs On Security





The Hacker News
 The Flood is Coming And The Pipes Were Already FullOn November 6, 2026Source: The Hacker NewsByAn update on Athena, and some unsolicited predictions on what's coming next On Saturday, Dario Amode… Read more An update on Athena, and some unsolicited predictions on what's coming next
On Saturday, Dario Amodei published We Must Pace the Frontier. I agree with him. Go read it if you haven't. I've spent the summer looking at what these models find, and the gap he describes between what they can do and what the rest of us are ready for is the one I've been staring at since May.
The hardest piece of his |
 Chainalysis Breach Exposes All Users' Credentials, Forces Shutdown of Key ServicesOn November 6, 2026Source: The Hacker NewsByBlockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cy… Read more Blockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cyber attack targeting its systems also exposed names, usernames, password hashes and live tokens for all users.
"While we investigated, we removed access to Reactor and Data Solutions," the company said. "At this time we continue to have no evidence that any investigations data has been accessed |
 Hackers Hide Linux Backdoor in Control Web Panel Server to Execute Commands Without LogsOn November 6, 2026Source: The Hacker NewsByA backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel f… Read more A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin's XLab said this week.
The backdoored web server executes commands that attackers send via web requests, and those requests never appear in its access logs. Installing it takes root access, so the attackers must already control the server. |
 Experts Demonstrate Barracuda Email Security Gateway Chain Enabling Root Access Without LoginOn November 6, 2026Source: The Hacker NewsByTwo flaws in Barracuda's Email Security Gateway, an email-filtering appliance, can be chained to run… Read more Two flaws in Barracuda's Email Security Gateway, an email-filtering appliance, can be chained to run commands on it as root, its highest level of access, with no login required.
The company released patches on Monday, and the security firm watchTowr detailed the attack chain on Thursday.
One flaw, CVE-2026-116606, is an authorization bypass. An unauthenticated attacker can use it to restore a |
 OpenSSH Issues Emergency Fix for Flaw Letting Long Passwords Bypass SSH Auth on Alpine LinuxOn November 5, 2026Source: The Hacker NewsByAttackers can log in to accounts that have no password, such as SSH key-only accounts, on some Alpin… Read more Attackers can log in to accounts that have no password, such as SSH key-only accounts, on some Alpine Linux servers running the standard openssh-server package. They need network access to the server, an account name, and a password between 257 and 1,024 bytes long.
OpenSSH, which rates the flaw critical, released version 10.6p2 today to block it. Alpine has published fixed packages for every |
 Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User InteractionOn November 5, 2026Source: The Hacker NewsByCybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploi… Read more Cybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploited to bypass Lockdown Mode protections in OpenAI ChatGPT.
Lockdown Mode was introduced by the artificial intelligence (AI) company in June 2026 as an optional setting to minimize data exfiltration risks arising from prompt injections.
"The flaw could enable silent chat data theft, phishing, |
 ThreatsDay: Apache OFBiz RCE, DreamHost Breach, DeFi Site Hijacks + 17 More StoriesOn November 5, 2026Source: The Hacker NewsByHow much damage can someone do without breaking much? Quite a lot, it seems. A stolen login can open… Read more How much damage can someone do without breaking much? Quite a lot, it seems. A stolen login can open doors across several systems. A trusted setting can be used to lock people out. Even a simple file copy can reach places it shouldn't. And while new tools are helping find security holes faster, some important systems are still taking months, sometimes over a year, to get patched. Not exactly a |
 Is Your Exposure Management Platform Leaving You Exposed? Five Tests to Find OutOn November 5, 2026Source: The Hacker NewsByA critical finding can move through several security tools and still leave the organization exposed.… Read more A critical finding can move through several security tools and still leave the organization exposed.
The vulnerability has a severity score, and a ticket has reached the queue. Progress then depends on information the finding may lack: who owns the system, whether attackers can reach it, what protection exists, and how a change could affect the business.
Each missing detail creates |
 OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits in 30-Hour RunOn November 5, 2026Source: The Hacker NewsByOpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intellige… Read more OpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intelligence (AI) model to validate and patch 948 local privilege escalation vulnerabilities in Linux for $1.2 million in API costs.
"Our prototype identified and analyzed 2,308 candidate Linux kernel findings, dynamically reproduced 1,724 vulnerabilities, and produced 948 local privilege escalation (LPE) |
 5 Active Cyber Threats That Put US Enterprises at Risk in October 2026On November 5, 2026Source: The Hacker NewsByOctober 2026 brought another wave of cyber threats targeting US businesses, with attackers exploitin… Read more October 2026 brought another wave of cyber threats targeting US businesses, with attackers exploiting trusted platforms, legitimate authentication processes, and everyday business workflows. For enterprises, these campaigns raise the stakes beyond individual security incidents, increasing the risk of financial losses, data breaches, and costly operational disruption.
Below, we examine five |
How Can We Help?